Trust Center
We keep your numbers. Never your words.
Third Degree is built for the conversations that can't leak. This page states exactly what we hold, what we never hold, who processes what, and how each claim can be verified.

Third Degree is built for the conversations that can't leak. This page states exactly what we hold, what we never hold, who processes what, and how each claim can be verified.

The whole pipeline on one page: where a session goes, what touches it, and the seven controls that stand between it and the ways it could be attacked. Read left to right. The numbered shields are keyed to the table beneath.
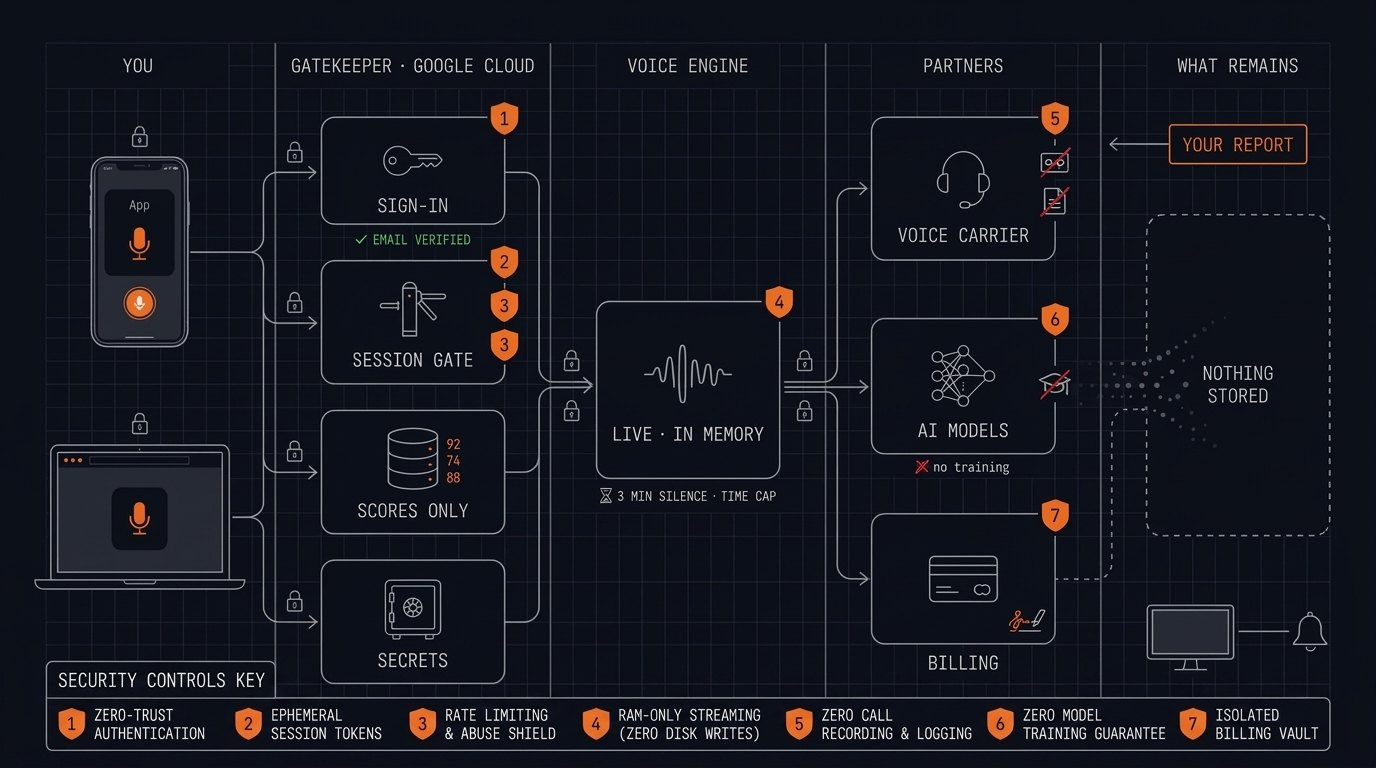
| # | Where | Attack vector | Countermeasure in place |
|---|---|---|---|
| 1 | Sign-in | Account takeover; anonymous or throwaway accounts used to burn sessions | Registered email accounts only, with email verification enforced before any session can start. No anonymous sessions exist. Sign-out and account deletion are inside the app on every screen a signed-in user can reach. |
| 2 | Session gate | Session-token replay or forgery; connecting to the voice engine without going through the gate | Every session is minted server-side as a one-time token that expires in two minutes and is marked used on first connect; a second use is refused. The engine's own connection additionally requires a secret bearer token held only in the secret store, so there is no path to it that skips the gate. |
| 3 | Session gate | Wallet abuse and runaway cost: burner accounts, scripted session floods, a call left open for hours | Per-user rate limits and daily quotas; per-device and per-IP allowances on the free Challenge (device fingerprinting there only); minute metering that refuses a session at zero and sizes each session to the balance that remains; a platform time cap enforced by the voice carrier itself; automatic hang-up after three minutes of silence. |
| 4 | Voice engine | Prompt injection through uploaded material; the AI quoting or leaking the document; anything written to disk | Your material is fenced as untrusted reference and the AI is directed to ignore any instructions embedded in it; an optional one-tap anonymization rewrites names to roles before use. The session lives in process memory for the duration of the call and is discarded at the end. No recording and no transcript are written anywhere on our side; only numbers leave. |
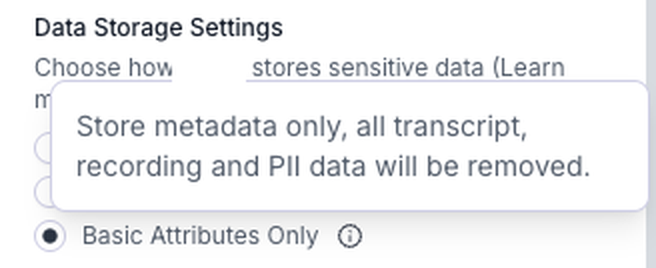
| 5 | Voice carrier | The voice vendor keeping recordings or transcripts | Configured account-wide to keep basic call attributes only: no recordings, no transcripts, no PII. Hard-coded into every call we create and mirrored in the vendor console. Console evidence is shown under Verification below. |
| 6 | AI models | Model providers training on your content or retaining it; a provider outage stranding a session | Paid API terms at every provider: your content is never used for training. Reached directly, with no gateway or reseller in between. One provider retains for abuse monitoring only, transiently; zero-retention status with that provider is requested. A failover chain across providers keeps a live session going if one is down. |
| 7 | Billing | Forged payments or entitlements; card data exposure | Every payment event arrives as a cryptographically signed webhook and is verified before anything is granted; entitlement fields cannot be written by any client (database rules); an unknown plan fails closed with no price rather than the cheapest one. Card data never touches our servers. |
Not on the diagram but everywhere on it: every hop is encrypted (TLS for all API traffic, mandatory real-time media encryption for the voice stream), API keys live in a managed secret store and never on a device, and a health probe checks every provider every few minutes and pages the founder directly when one fails.
| Processor | Role | Session substance retained |
|---|---|---|
| Voice infrastructure | Carries the live call between you and the AI. Reached directly, no gateways or resellers. | None — configured account-wide to keep call attributes only: no recordings, no transcripts (verified, see below) |
| Language-model providers | Frontier models from the world's leading labs — the examiner, the witness, the report. Reached directly. | Not stored by us, not used for training. Provider terms allow transient retention for abuse monitoring only (up to 30 days at one provider, shorter at the other). Zero-retention status with that provider is on our roadmap below. |
| Google Firebase | Authentication, database, functions, hosting | None — numeric results and account data only |
| Stripe | Payments (web) | None — billing data only, no session access |
| RevenueCat | App Store subscription management (iOS) | None — purchase receipts and entitlement state only |
| Fingerprint | Device identification for fraud prevention — keeps the free Challenge to one daily allowance per device, not per throwaway account | None — browser/device signals only; never audio, words, or material |
Every system your session touches is audited by someone other than us. The reports are distributed under each vendor's non-disclosure terms, so they are not reproduced here — but each one is either self-serve or a request away, and we will forward any of them to your reviewer.
| Processor | Standards held | Where to get the report |
|---|---|---|
| Google Cloud & Firebase | SOC 1, SOC 2, SOC 3 · ISO 27001, 27017, 27018 | Self-serve: Google Cloud Compliance Reports Manager · Firebase privacy & security |
| Voice infrastructure | SOC 2 Type II · HIPAA | On request under NDA. We name the vendor and forward the report to your security reviewer: security@thirddegreeprep.com |
| Language-model providers | SOC 2 Type II (each) | On request under NDA, as above. One provider's report is self-serve from its trust portal once you accept its NDA; we will point your reviewer to it. |
| Stripe | PCI DSS Level 1 · SOC 1 & SOC 2 | Self-serve: Stripe security & compliance |
| RevenueCat | SOC 2 Type II | On request from the vendor; we will forward it. RevenueCat privacy |
| Fingerprint | SOC 2 Type II · ISO 27001 | Self-serve: Fingerprint security |
For your security review. Alongside the reports above we can provide a completed industry-standard self-assessment (CAIQ or SIG Lite), the configuration evidence behind the verification items below, and a contractual zero-retention warranty in pilot and enterprise agreements. Ask at security@thirddegreeprep.com.
| Item | Status |
|---|---|
| Vendor storage disabled (voice recordings & transcripts) — console evidence below | ACTIVE — RE-VERIFIED SEPTEMBER 2026 |
| Historical vendor data purged (zero recordings held) | COMPLETED — VERIFIED JULY 2026 |
| Database holds no session text (numeric results only) | ACTIVE — VERIFIED JULY 2026 |
| Independent counsel attestation (privilege & privacy review, co-signed, published here) | IN PROGRESS |
| Zero Data Retention status with the language-model provider that retains for abuse monitoring | REQUESTED — SEPTEMBER 2026 |
| Independent technical verification of zero-retention claims (CPA agreed-upon procedures) | PLANNED |
| Completed CAIQ / SIG Lite self-assessment | PLANNED |
| SOC 2 | ON THE ENTERPRISE ROADMAP |
If we ever receive a legal demand for session content, our position is structural, not just policy: we do not hold it and no mechanism exists to retrieve it. We can produce only what exists — numeric scores and account metadata.
Security disclosures: security@thirddegreeprep.com · Privacy questions: privacy@thirddegreeprep.com · Full policy: Privacy Policy